Attacks on founders and consultants have grown past phishing emails. They now show up as live LinkedIn intro calls. This post breaks down a fake podcast guest invitation built to install Atomic macOS Stealer (AMOS) on Apple computers.
It covers how the trick works, how attackers hide behind lookalike domains, and the red flags to watch for, so you can protect your passwords and your crypto assets.
_____________________________________________________________
Quick Answers – Jump to Section
- It Started with a Flattering Invitation
- Then the Call Took a Strange Turn
- What the Link Really Did
- The Part That Stings
- The Pattern (How to Spot It)
- What to Do If You’re Targeted
- Final Thoughts
- Frequently Asked Questions
__________________________________________________________
It Started with a Flattering Invitation
A connection messaged me on LinkedIn. His profile looked legit. He had over 500 connections and a believable job title. He said he was working with Blockworks on a new podcast about people’s own crypto stories, nothing to do with work or markets. Was I interested?
I thought it would be a good opportunity to share my experience from 2022 when my crypto account was drained by thieves who stole my iPhone. I agreed to be a guest.
It sounded completely plausible. It is the kind of offer many founders and consultants say yes to. So we booked a call.
Founders build a public profile for good reasons, and the LinkedIn growth tactics web3 founders use to attract investors show how visible that profile has become. Attackers read it too.
__________________________________________________________
Then the Call Took a Strange Turn
When I joined, he was not there. A woman was on the line instead. That was red flag number one.
We started talking. Within two minutes, she told me to click a specific link to start the recording session properly.
I told her we were already on a working call.
Her reply: “No, we can’t host it on Google.”
That one sentence is the whole scam. We were already connected on a platform that worked fine, yet I was told it was not good enough.
__________________________________________________________
What the Link Really Did
I was curious enough to look at the URL, but careful enough not to click it. Instead, I ran the domain through a security check.
The landing page claimed my meeting software was out of date and pushed an automatic download.
It was malware. Specifically, it was Atomic macOS Stealer, also called AMOS. It is built to empty your Keychain, grab browser passwords, copy session cookies, and drain crypto wallets.
Here is what I found:
- Domain: mefex[.]space
- Age: registered about six weeks earlier
- Hosting: hidden behind Cloudflare and privacy proxies
- Threat level: high, and flagged in Security Alliance reports alongside the lookalike domains mefex[.]app, mefex[.]me, and mefex[.]online
Attackers burn and swap these lookalike domains as soon as researchers flag them. Wallet drains are the prize here, which is why the ways AI agents now guard web3 wallets are worth a look.
__________________________________________________________
The Part That Stings
Earlier that same morning, I had been updating key email passwords in my Mac’s Keychain.
If I had clicked that download button, AMOS could have taken every saved password at once. I would have had no warning until accounts started to fall.
That is the core danger of modern social engineering. It does not ask for your password. It only needs you to run one file.
__________________________________________________________
The Pattern (How to Spot It)
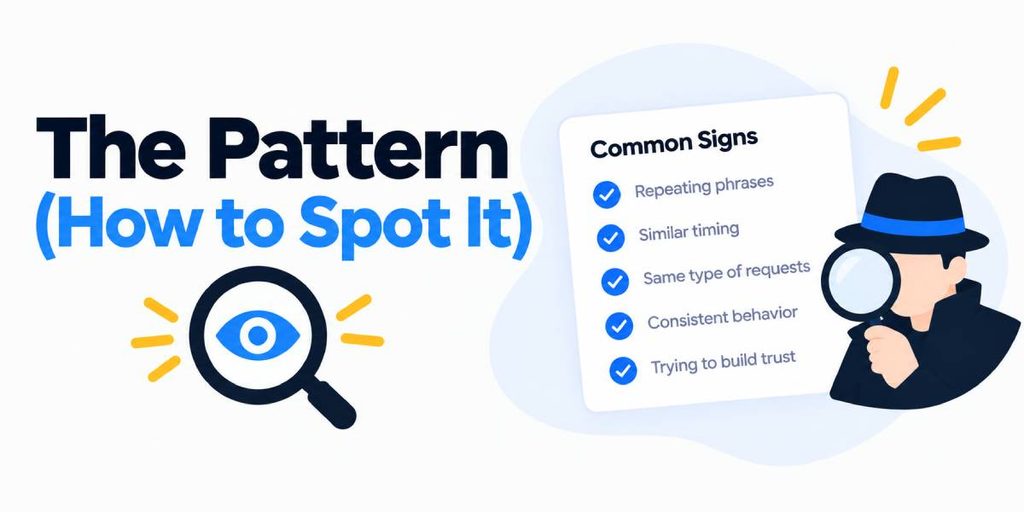
This campaign targets business owners, agency founders, web3 creators, and consultants. It uses your public credibility against you.
| Attack stage | What the attacker does |
|---|---|
| 1. First contact | Sends a warm, flattering LinkedIn invite to be a podcast guest |
| 2. Building confidence | Books a real intro call to lower your guard |
| 3. The pivot | Pushes you off Zoom or Google Meet and onto a custom link |
| 4. The payload | Prompts a “required update” download |
In my case, they even borrowed the branding of a real podcast and media company, so a quick background search looked fine.
Watch for these red flags:
- The host you booked is missing from the call
- You are asked to leave a working platform within minutes
- A page says your meeting software needs an update
- The link uses an odd domain that looks nearly right
Patterns like these can be caught early, and how AI spots fraud patterns in real time across web3 shows where detection is heading.
__________________________________________________________
What to Do If You’re Targeted
Never install a custom meeting app to join a call you did not set up. Real media outlets and podcasts use Zoom, Google Meet, or Riverside. No real host needs custom software for a basic interview.
If this lands in your inbox:
- Do not click the link or download any files.
- Screenshot the full conversation as a record.
- Report and block the account on LinkedIn right away.
- Do not engage or call them out. Replying confirms your account is active and can put you on a target list.
If you already downloaded a suspicious file, disconnect your device from the network right away. Reset your passwords from a clean machine, and audit your system.
Small teams often skip basic protections too, and the security habits small crypto teams tend to skip make a handy checklist.
__________________________________________________________
Final Thoughts
I caught this because I was suspicious early and had the tools to check the URL before opening it. Many busy founders do not get that buffer. You are jumping between tasks, the invite is flattering, and the link looks harmless.
The threat has changed. Real attacks are no longer sitting in your spam folder. They hide inside friendly meeting invites and casual chats. Know what to look for before one lands in your inbox.
If you want to protect your brand’s online presence and spread your message across search and AI engines, our Growth Engine Blueprint lays out the multi-format distribution system and messaging framework to follow.
__________________________________________________________
Frequently Asked Questions
What is Atomic macOS Stealer (AMOS)?
AMOS is malware built to target Apple computers. Once it runs, it takes saved browser passwords, auto-fill data, macOS Keychain passwords, system files, and crypto wallet extensions, without asking for an admin password.
Why do attackers use fake podcast invitations?
Flattery and professional networking lower your guard. Founders and consultants are used to booking guest interviews, so attackers use live calls to add pressure and push you to click a bad meeting link.
How do I verify that a podcast host is legitimate?
Cross-check the host and producer on official company channels or verified social profiles. Real podcast producers record on standard platforms like Zoom, Google Meet, Riverside, or SquadCast. They never demand a custom download to join a call.
What should I do if I already clicked a suspicious meeting download link?
Disconnect your device from Wi-Fi and the network right away. Use a separate, clean device to change your passwords, especially email, financial, and crypto accounts. Then revoke active web session tokens and run a full malware sweep or system wipe.
_________________________________________________________________
Download your free copy of the Growth Engine Blueprint here and start accelerating your leads.
Want to know how we can guarantee a mighty boost to your traffic, rank, reputation and authority in you niche?
Tap here to chat to me and I’ll show you how we make it happen.
If you’ve enjoyed reading today’s blog, please share our blog link below.
Do you have a blog on business and marketing that you’d like to share on influxjuice.com/blog? Contact me at rob@influxjuice.com.
Latest Blogs
- How to Edit Professional Videos for Your Business on a Budget
- The Fake Podcast Scam: How a LinkedIn Invitation Nearly Put Malware on My Mac
- Why Google Is Turning Into an Answer Engine, and What It Means for Web3 Teams
- Why Web3 Teams Are Turning to Gamma to Build Decks and Docs Faster
- Cyber5 Prep for Web3 Brands: Get Your Paid Media Ready Before Costs Spike